Overview
To use Secure Boot, TPM 2.0 needs to be turned on, your Windows disk must be set to GPT, and your BIOS to UEFI. When these requirements are met, you can enable Secure Boot from your PC’s Advanced startup. Follow the steps in this guide for help enabling Secure Boot and checking if your PC meets the requirements.
What’s Secure Boot?
Secure Boot is a built-in security feature for Windows PCs that makes sure your computer only uses trusted software when it starts up.EA requires Secure Boot on certain games to prevent unauthorized third-party programs or cheat software from loading before your game runs.Secure Boot allows games supported by EA Javelin Anticheat to detect and remove bad actors, resulting in fewer cheaters and a better experience for players.
How do I check if Secure Boot’s enabled?
On Windows 10 and Windows 11:- 1Select the Windows Key + R. This will open the Run Window.
- 2Type msinfo32 and select the Enter Key or OK.
- 3From the System Information window that opens, select System Summary.
- 4Scroll down to find these values:
- BIOS Mode value should be UEFI
- Secure Boot State value should be On.

- If Secure Boot State is Off, we’ll need to check the BIOS Mode and then enable it.
- If Secure Boot State is Unsupported, check with your motherboard manufacturer’s specification sheet or manual to see if Secure Boot is supported.
- If BIOS Mode is UEFI, then you can move on to how to enable Secure Boot.
- If BIOS Mode is Legacy, you’ll need to check if your Windows disk is MBR or GPT.
Heads up: your Windows install drive must be set up correctly to support Secure Boot. Secure Boot needs to use GPT (GUID Partition Table) instead of MBR (Master Boot Record).
If Windows displays "Secure Boot is enabled but not active," you usually need to reset your Secure Boot keys.Restart your PC and press your BIOS setup key (usually F2, F12, or Del) to open the BIOS menu.
- 1Go to the Security or Boot tab.
- 2Select Secure Boot.
- 3Choose Key Management or Secure Boot Mode.
- 4Select Restore Factory Keys or Reset to Setup Mode, then choose Install Default Keys.
- 5Save your settings and restart your PC.
This happens when your BIOS is in Setup Mode instead of User Mode.
- 1Open your BIOS menu during startup.
- 2Go to Secure Boot settings.
- 3Choose Secure Boot Mode and change it from Custom to Standard (or select Install Default Secure Boot Keys). This automatically switches the system status to User Mode.
- 4Save your changes and exit.
Secure Boot requirements
Secure Boot needs your PC to run on a UEFI partition style known as GPT (GUID Partition Table). If your hard drive is currently formatted as MBR (Master Boot Record), you’ll need to convert it before you can enable Secure Boot.Heads-up: This article is a general guide, but it might not follow the exact steps of your PC.Back up your data before proceeding. While converting your partition style from MBR to GPT is generally safe, we strongly recommend backing up all important files to an external drive or cloud storage first to prevent any accidental data loss.If you’re not used to navigating to and updating your BIOS settings, you should contact a professional or your manufacturer’s customer support. Incorrectly configuring BIOS settings can cause issues with your computer, including failure to start up.We highly recommend that you read your computer or motherboard manufacturer's support resources before updating any BIOS settings. EA doesn’t take responsibility for changes to your BIOS settings.
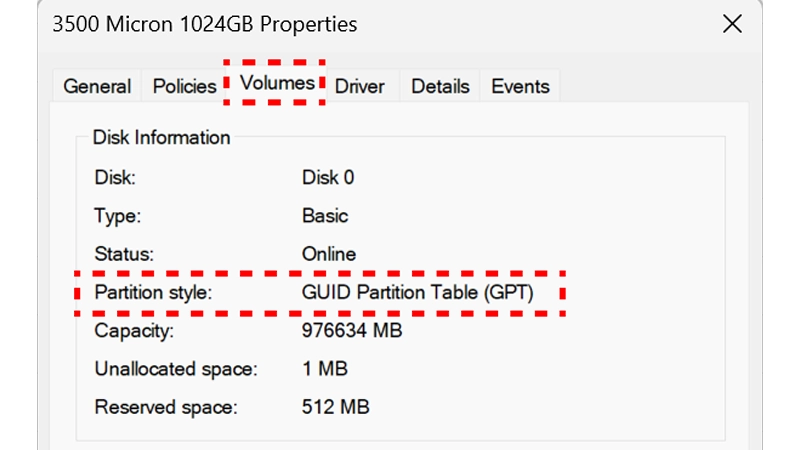
- 1Open the Windows Start button and choose Disk Management.
- 2Select your primary system disk (usually Disk 0) and choose Properties.
- 3Select the Volumes tab and check the Partition style line to see if it's MBR or GPT.
- If it's MBR, open the Windows search bar, type cmd, and choose Run as administrator.
- 4Type mbr2gpt /validate /allowFullOS and press Enter to verify compatibility.
- 5If the validation passes, type mbr2gpt /convert /allowFullOS and press Enter to convert your partition style.
- 6Once completed, restart your PC, open your BIOS menu, and change your Boot Mode from Legacy BIOS to UEFI.
Refer back to your manufacturer for guidance
Remember, every manufacturer is different, and if at any point when following the steps in this article your PC doesn’t match our instructions, you should refer back to your manufacturer's support resources. Here are links to some of the various manufacturers' guides:General support: Acer SupportSecure Boot, TPM 2.0, and UEFI BIOS: Acer Secure Boot Desktop / Acer Secure Boot Laptop
General support: Dell SupportSecure Boot: Dell Secure BootTPM 2.0: Dell TPM 2.0UEFI BIOS: Dell UEFI BIOS
General support: ASUS SupportSecure Boot: ASUS Secure BootTPM 2.0: ASUS TPM 2.0UEFI BIOS: ASUS UEFI BIOS
General support: ASRock SupportSecure Boot, TPM 2.0, and UEFI BIOS: ASRock Secure Boot
General support: Corsair SupportSecure Boot, TPM 2.0, and UEFI BIOS: How to Fix Secure Boot and TPM 2.0
General support: Dell SupportSecure Boot: Dell Secure BootTPM 2.0: Dell TPM 2.0UEFI BIOS: Dell UEFI BIOS
General support: GIGABYTE SupportSecure Boot: GIGABYTE Secure BootTPM 2.0 and UEFI BIOS: GIGABYTE Windows Security Features
Search for Secure Boot, TPM 2.0, or UEFI BIOS: HP Support
General support: Lenovo SupportSecure Boot: Lenovo Documentation CenterTPM 2.0: Lenovo TPM 2.0UEFI BIOS: Lenovo UEFI
General support: MSI SupportSecure Boot: MSI Secure BootTPM 2.0: MSI TPM 2.0UEFI BIOS: MSI UEFI BIOS
General support: HP SupportSecure Boot, TPM 2.0, and UEFI BIOS: HP PCs – OMEN BIOS setup utility information and menu options | HP® Support
Check TPM
Check your Windows disk
Check BIOS
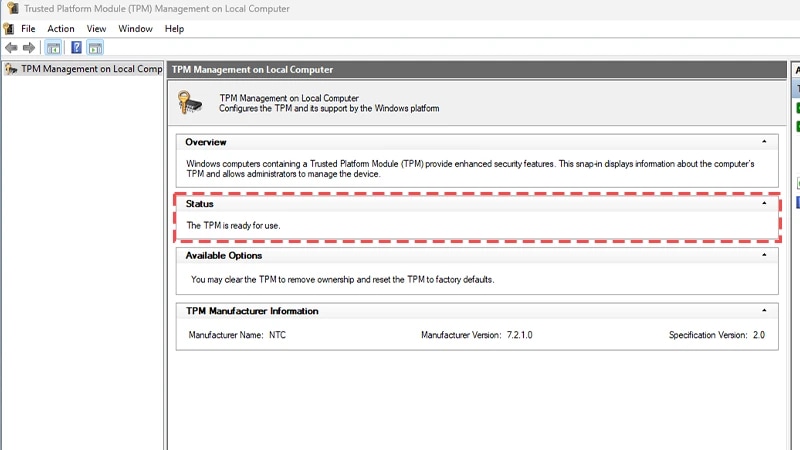
Check if TPM 2.0 is enabled
- 1Select the Windows key and R at the same time to bring up Run Windows.
- 2Type tpm.msc and select the Enter Key.
- 3Check the Status box to see if TPM is ready to use. If it’s ready to use, it’s time to check if your Windows disk is MBR or GPT.
- 4If TPM isn’t ready, refer to your manufacturer on how to correctly enable TPM on your device.



How do I enable Secure Boot?
Before following these steps, make sure both the TPM 2.0 and UEFI requirements have been successfully enabled.Remember—the BIOS menus for different brands and motherboard manufacturers can differ from those pictured here, so make sure to refer to your manufacturer’s support resources for specifics.
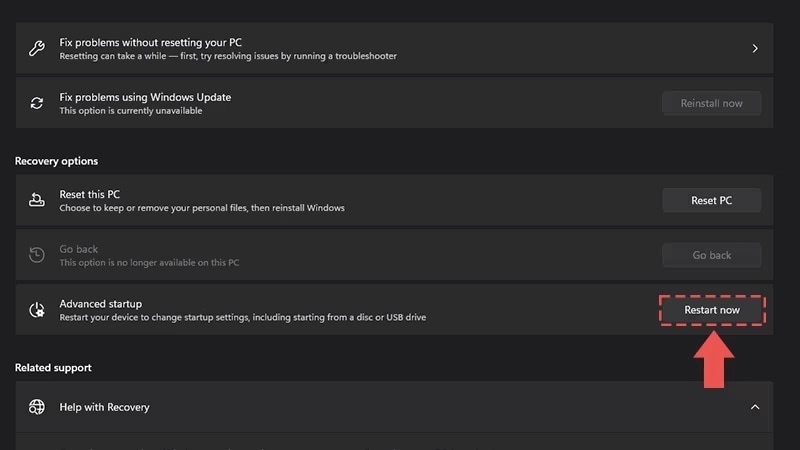
- 1Select the Windows Key and search for Change Advanced Startup Options.
- 2Next to Advanced startup select Restart now. Your computer will restart into Advanced Startup.
- 3Select Advanced options.
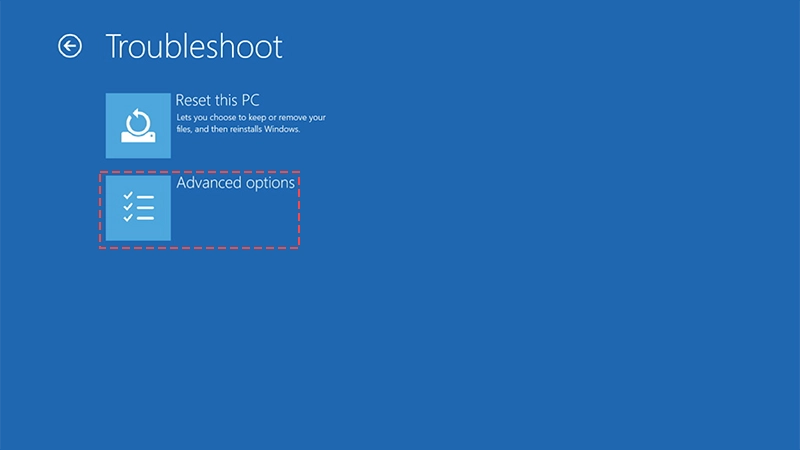
- 4Select UEFI Firmware Settings.

- 5This will enter into your BIOS which should look similar to the following but often differs from one manufacturer to another.

- 6Navigate to the Boot tab, if you are having difficulty finding the correct option, many BIOS have a search function that you can use to find the correct tab and setting Pictured above the search can be accessed by hitting F9.
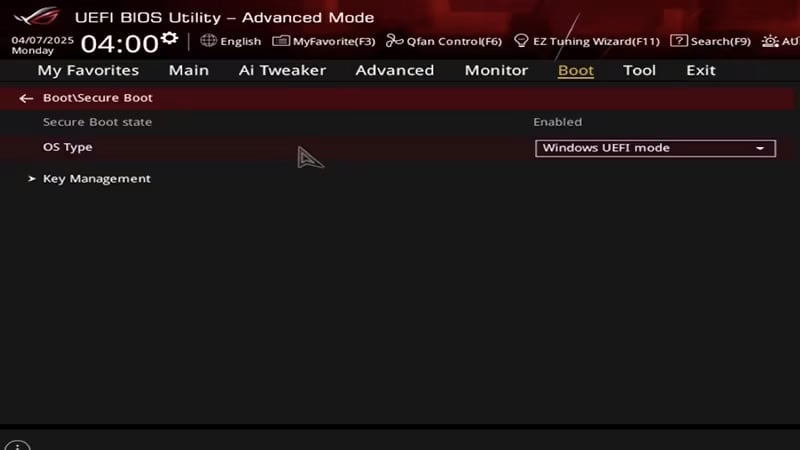
- 7Secure Boot state should be Enabled.
- If it’s set to Disabled, change it to Enabled.
- Note: If you can’t modify the setting you need to refer to your manufacturer for guidance. It's not uncommon for some manufacturers to require that you reset the Secure Boot Keys to factory values or enable the admin password for your Bios before allowing settings to be changed.
- 8OS Type should be set to Window UEFI mode.
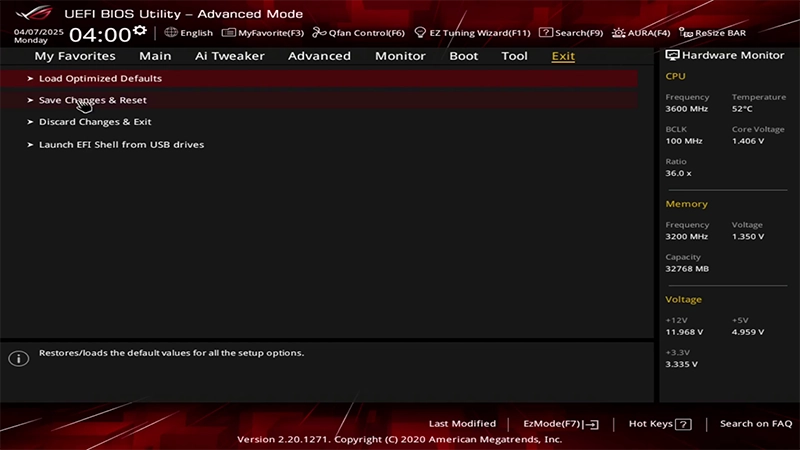
- 9Go to the Exit tab and select Save Changes & Reset.
- 10On the resulting confirmation dialog, Select Ok.
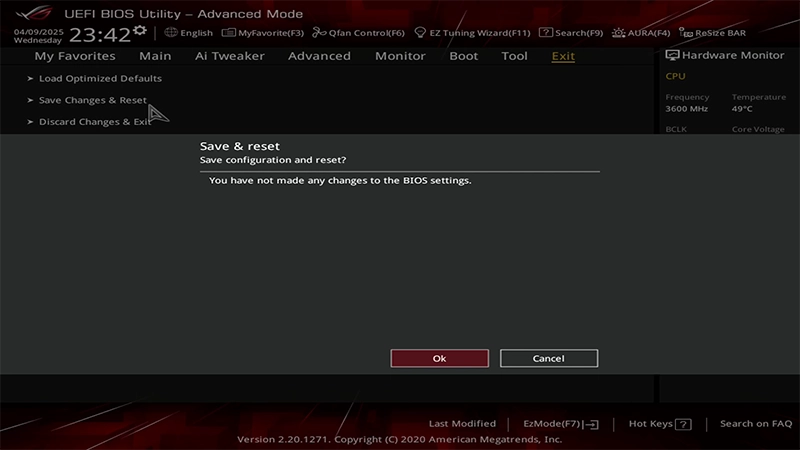
- 11Your PC will restart with Secure Boot turned on.
Secure Boot requires UEFI. If your system only supports Legacy BIOS, you won't be able to turn on Secure Boot. You need to upgrade your motherboard or hardware to a system that supports UEFI to play games that require Secure Boot.
Certain games, like EA SPORTS FC™ and games that use EA Javelin anticheat, require Secure Boot on Windows 11 to ensure a fair and secure gaming environment.To find out if your game uses EA Janelin anticheat,
- 1Choose your game from the EA app.
- 2Select Manage, then View Properties.
- 3Choose Browse.
- If your game uses EA Javelin anticheat, the files will be visible in this folder.
Secure Boot is an official Microsoft Windows security feature designed to block malware, rootkits, and unauthorized software from infecting your PC during startup. Turning it on won’t harm your files or system performance.